Conditional ownership
Everything depends on one door.
Lose the account, face an API change, or meet an unaffordable exit—and your data may no longer feel like yours.
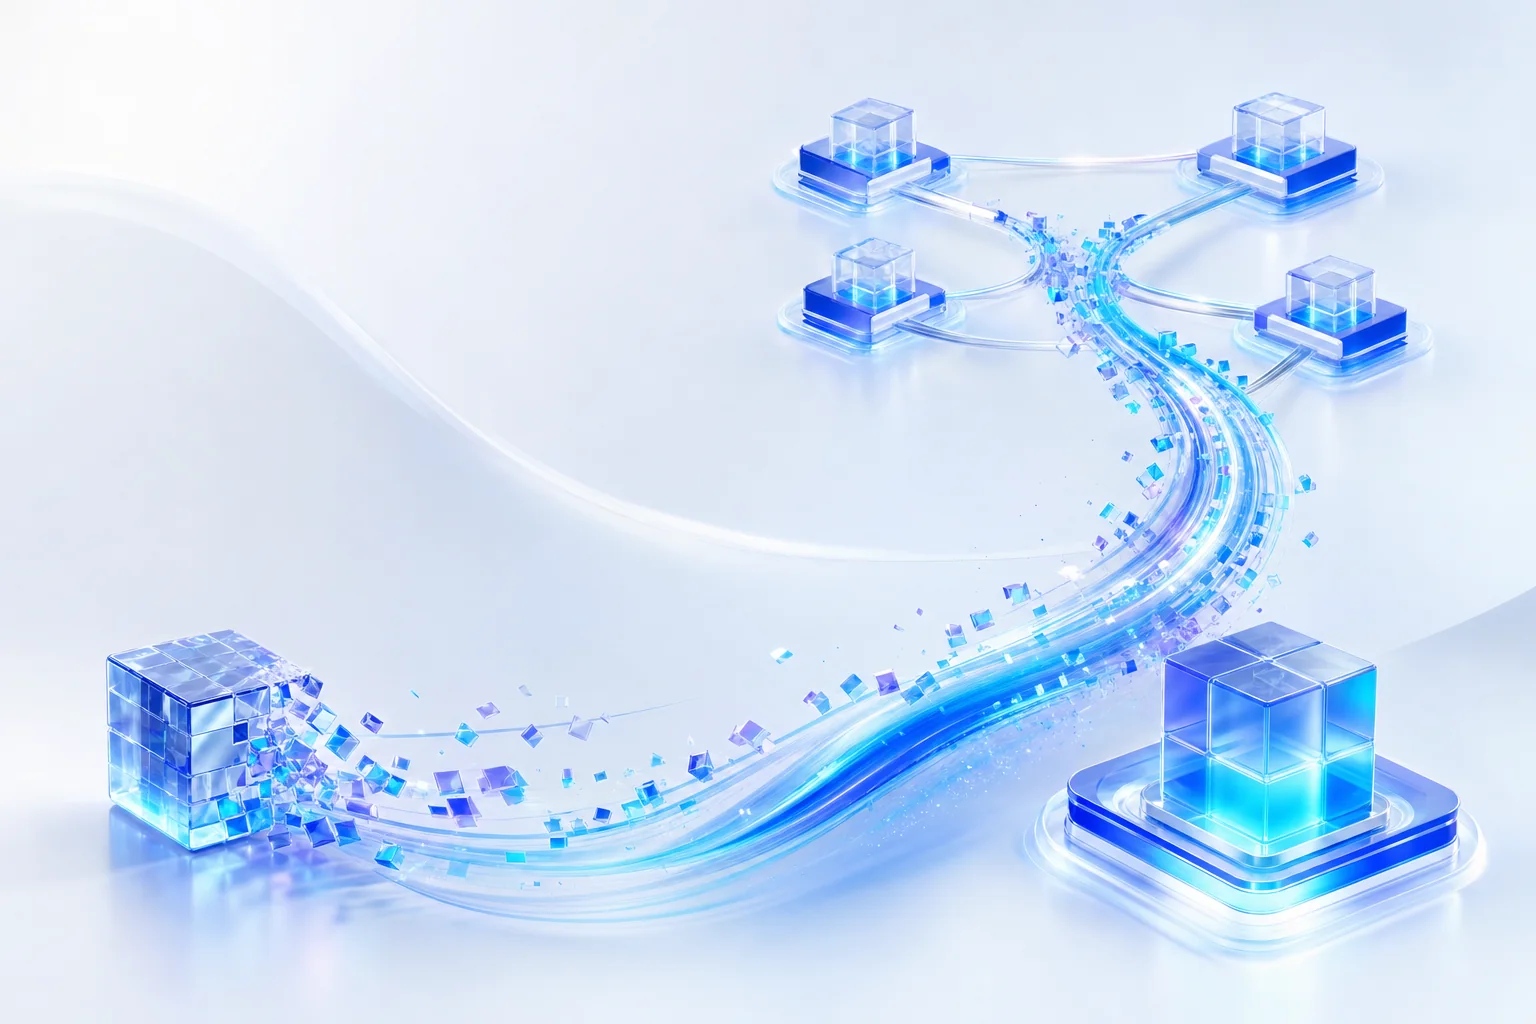
Encrypt before upload. Check that your data is safe. Move it whenever you want—without depending on one company.
Plaintext and keys never need to reach a storage node.
THE REAL PROBLEM
If one company controls your login, encryption keys, permissions, and export button, your data is only yours until they say otherwise.
Lose the account, face an API change, or meet an unaffordable exit—and your data may no longer feel like yours.
SOVRA separates content, authorization, and storage contracts so each can move without rebuilding everything.
Client-side encryption means storage nodes receive ciphertext—not your plaintext or master key.
Unpredictable challenges and real retrieval audits measure possession, recoverability, and service quality separately.
Exportable manifests and open formats let compatible clients verify, recover, and relocate your objects.
Regional nodes and encrypted edge caches target hot data where latency and egress costs actually matter.
HOW IT WORKS
SOVRA encrypts it, splits it, spreads it, checks it, and puts it back together when you need it.
A fresh data key encrypts the object before it leaves your trust boundary. Keys stay under your device, recovery shares, or enterprise KMS.
Encryption, upload, retrieval, caching, and repair.
Policy, routing, proofs, indexing, and observability.
Compact commitments, escrow, registration, and governance on Solana.
BUILT FOR DATA THAT MATTERS
SOVRA is designed for important, private, long-lived data that must stay available across products and providers.
Private, versioned memory that stays recoverable when devices, models, or agent providers change.
Encrypted media, assets, replays, snapshots, and user content with verifiable references.
Independent proofs, recovery drills, regional policy, and export records for critical backups.
Cache hot ciphertext near users or dual-write with existing object storage for an independent recovery path.
THE COORDINATION LAYER
SOVR supports payment, performance collateral, verifiable supply incentives, and governance. It is not equity, revenue share, or a promise of returns.
Allocation is a proposed framework subject to final on-chain arrangements.
Storage, retrieval, bandwidth, and premium services.
Collateral aligned to the service risk a node can create.
Verified service—not idle capacity or token holdings alone.
Parameters, Treasury, ecosystem funding, and upgrades.
The SOVRA whitepaper explains the technology and SOVR utility. It is not a token offer or investment advice.
ROADMAP BY EVIDENCE
Each phase advances only when security, performance, economics, and real demand support it.
Encrypted objects, manifests, coding, basic nodes, proof experiments, and fault recovery.
Upload, retrieval, registration, escrow, monitoring, and an SDK alpha using test data.
Multi-region nodes, retrieval audits, repair, staking, security review, and controlled paid pilots.
Edge, S3 Gateway, enterprise KMS, payment options, broader nodes, and progressive governance.
STRAIGHT ANSWERS
No. Large files, detailed proofs, and high-frequency telemetry stay off-chain. Solana records compact commitments, payments, node registration, governance, and proof summaries.
Not under the default model. Data is encrypted before upload, and ordinary storage nodes receive ciphertext without your decryption keys.
No. The early focus is workloads that benefit from sovereign keys, independent verification, migration, wallet-native access, or regional service. Hybrid and dual-write deployments are part of the design.
Possession alone is not enough. SOVRA separates possession proofs, full retrieval audits, and service-quality measurements so recoverability and timely reads can be tested directly.
SOVRA is being built in phases. Each stage must pass implementation, testing, independent security assessment, and legal review before production use.
Users choose a recovery model: full self-custody, device plus recovery shares, or enterprise KMS. Full self-custody can be unrecoverable, so the product must make that responsibility explicit.
THE SOVEREIGN DATA LAYER
Discover a simpler way to keep important data private, verifiable, and ready to move.
Download whitepaper v1.1